How Security Frameworks Respond to Digital Threats: The Silent Shield Against Cyber Chaos
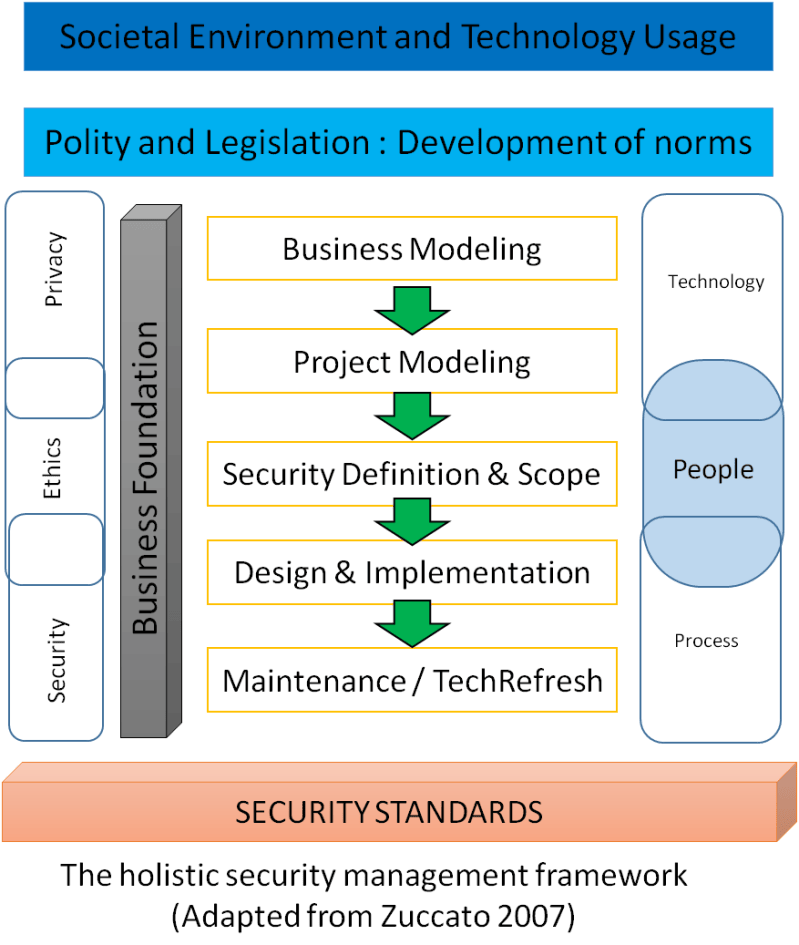
Cyberattacks no longer lurk in the shadows—they strike with surgical precision, exploiting vulnerabilities in real time. The difference between a breach and a fortress now hinges on whether an organization’s security frameworks can respond to digital threats with agility, not just reactiveness. Traditional perimeter defenses are obsolete; today’s threats demand frameworks that anticipate, adapt, and neutralize risks before they materialize.
Consider the 2023 CrowdStrike outage, where a single misconfiguration cascaded into global chaos, or the rise of AI-powered phishing campaigns that bypass legacy filters. These incidents expose a harsh truth: static security measures fail against dynamic adversaries. The most resilient organizations don’t just deploy tools—they architect security frameworks designed to respond to digital threats with layered intelligence, automated countermeasures, and human oversight.
Yet despite the urgency, many frameworks remain siloed, reactive, or overly complex. The gap between theory and execution is widening as threats evolve. This analysis dissects how modern security frameworks—from NIST CSF to MITRE ATT&CK—operate, their measurable advantages, and why the future lies in predictive, self-healing architectures.
The Complete Overview of Security Frameworks Responding to Digital Threats
Security frameworks are no longer optional—they are the operational backbone of digital risk management. At their core, these structured approaches provide a methodical response to digital threats by aligning people, processes, and technology. Unlike point solutions (e.g., firewalls or antivirus), frameworks offer a holistic blueprint: identifying vulnerabilities, prioritizing risks, and deploying countermeasures in a scalable manner.
The shift toward proactive threat response frameworks marks a departure from compliance-driven models. Organizations now prioritize frameworks that integrate real-time analytics, threat intelligence feeds, and automated incident response. The result? A closed-loop system where anomalies trigger immediate containment, reducing dwell time from hours to seconds. This evolution is critical, as the average cost of a data breach surpassed $4.45 million in 2023—a figure that frameworks with adaptive response capabilities can mitigate.
Historical Background and Evolution
The origins of structured security frameworks trace back to the 1990s, when the U.S. Department of Defense introduced the Rainbow Series, a foundational set of guidelines for protecting classified systems. These early models emphasized access control and encryption but lacked the agility needed for modern cyber threats. The turning point came in 2014 with the National Institute of Standards and Technology’s Cybersecurity Framework (NIST CSF), which introduced a risk-based, iterative approach to responding to digital threats.
Table of Contents
- The Complete Overview of Security Frameworks Responding to Digital Threats
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How do security frameworks differ from traditional cybersecurity tools?
- Q: Can small businesses benefit from security frameworks?
- Q: How often should a security framework be updated?
- Q: What’s the role of AI in modern security frameworks?
- Q: How do frameworks handle supply chain attacks?
Parallel developments in the private sector saw frameworks like ISO 27001 and COBIT evolve from compliance checklists to dynamic risk management systems. The 2010s brought a paradigm shift: frameworks began incorporating threat intelligence (e.g., MITRE ATT&CK) and automation (e.g., SOC 2.0). Today, the most effective frameworks—such as the Zero Trust Architecture (ZTA)—operate on the principle of "never trust, always verify," fundamentally altering how organizations frameworks respond to digital threats in hybrid cloud environments.
Core Mechanisms: How It Works
The operational efficacy of a security framework hinges on three interconnected layers: detection, response, and recovery. Detection relies on behavioral analytics and anomaly detection (e.g., SIEM tools like Splunk or Darktrace), while response automates containment via playbooks (e.g., Microsoft Sentinel). Recovery, the often-overlooked phase, ensures systems return to a secure state without residual vulnerabilities—a process governed by frameworks like ITIL 4’s incident management.
What distinguishes high-performing frameworks is their ability to orchestrate a coordinated response to digital threats. For instance, a framework like CIS Controls integrates with EDR/XDR solutions to isolate compromised endpoints, while the MITRE ATT&CK framework—a knowledge base of adversary tactics—enables red teams to simulate attacks and refine defenses. The synergy between these mechanisms ensures that threats are neutralized before they escalate, reducing both financial and reputational damage.
Key Benefits and Crucial Impact
Organizations that deploy frameworks capable of actively responding to digital threats achieve more than just compliance—they gain a competitive edge. The measurable impact includes reduced breach costs, faster incident resolution, and enhanced customer trust. For example, a 2022 Ponemon Institute study found that companies with mature frameworks experienced a 50% lower average breach cost compared to peers relying on ad-hoc measures.
The strategic value extends beyond risk mitigation. Frameworks like NIST CSF and ISO 27001 provide a structured pathway for digital transformation, ensuring security aligns with business objectives. In sectors like healthcare or finance, where regulatory scrutiny is intense, these frameworks serve as a defensible response to digital threats that meets both internal and external audit requirements.
— "Security frameworks are the difference between a breach and a breach that becomes a headline."
— Gartner, 2023 Cybersecurity Leadership Report
Major Advantages
- Threat Anticipation: Frameworks like MITRE ATT&CK use adversary playbooks to predict attack vectors, enabling preemptive hardening.
- Automated Response: Integration with SOAR (Security Orchestration, Automation, and Response) tools reduces mean time to detect (MTTD) and resolve (MTTR) incidents.
- Regulatory Alignment: Compliance frameworks (e.g., GDPR, HIPAA) ensure legal safeguards are embedded into security operations.
- Scalability: Modular designs (e.g., NIST CSF’s "Identify-Protect-Detect-Respond-Recover") adapt to organizational growth without architectural overhaul.
- Cost Efficiency: Proactive frameworks cut breach costs by 40–60% through early detection and automated mitigation.

Comparative Analysis
| Framework | Strengths vs. Weaknesses |
|---|---|
| NIST CSF | Strengths: Flexible, risk-based, widely adopted. Weaknesses: Requires customization for specialized industries. |
| ISO 27001 | Strengths: Global standard, audit-ready. Weaknesses: Process-heavy, less agile for rapid threat response. |
| MITRE ATT&CK | Strengths: Adversary-centric, enhances red/blue teaming. Weaknesses: Not a standalone framework; requires integration. |
| Zero Trust (ZTA) | Strengths: Micro-segmentation, identity-first security. Weaknesses: High implementation complexity, tooling dependencies. |
Future Trends and Innovations
The next frontier in security frameworks responding to digital threats lies in AI-driven autonomy and quantum-resistant cryptography. Frameworks will increasingly leverage generative AI to simulate attack scenarios and generate adaptive countermeasures in real time. For example, Darktrace’s "Antigena" uses machine learning to autonomously neutralize threats without human intervention—a capability that will become standard in enterprise frameworks.
Quantum computing poses both a threat and an opportunity. While Shor’s algorithm could break RSA encryption, post-quantum cryptography (e.g., NIST’s CRYSTALS-Kyber) is being integrated into frameworks like ISO/IEC 27001 to future-proof data integrity. Additionally, frameworks will adopt immutable infrastructure—where systems self-heal by rolling back to known-good states—a direct response to the rise of ransomware-as-a-service (RaaS) attacks.

Conclusion
The evolution of security frameworks from static checklists to dynamic, threat-aware systems reflects a fundamental truth: responding to digital threats is no longer a reactive endeavor but a strategic imperative. Organizations that treat frameworks as living ecosystems—continuously updated, tested, and integrated—will outpace those relying on legacy defenses. The cost of inaction is no longer theoretical; it’s measured in stolen data, operational downtime, and eroded trust.
As threats grow more sophisticated, the frameworks that thrive will be those that blend human expertise with machine precision. The goal isn’t perfection—it’s resilience. And in the digital age, resilience is the only acceptable standard.
Comprehensive FAQs
Q: How do security frameworks differ from traditional cybersecurity tools?
A: Traditional tools (e.g., firewalls, antivirus) address specific threats but lack cohesion. Frameworks like NIST CSF or Zero Trust provide a structured response to digital threats by integrating tools, policies, and processes into a unified strategy, ensuring holistic protection.
Q: Can small businesses benefit from security frameworks?
A: Absolutely. Frameworks like CIS Controls offer scalable, low-cost implementations tailored to SMBs. The key is starting with foundational controls (e.g., inventory management, access restrictions) before expanding to advanced threat response.
Q: How often should a security framework be updated?
A: Continuous updates are critical. Frameworks should be reviewed quarterly for new threats (e.g., emerging malware families) and annually for regulatory changes. Automated compliance tools (e.g., Drata) streamline this process.
Q: What’s the role of AI in modern security frameworks?
A: AI enhances frameworks by enabling predictive threat response. Tools like Darktrace’s "Antigena" use unsupervised learning to detect and neutralize anomalies in real time, while AI-driven SOAR platforms automate incident containment.
Q: How do frameworks handle supply chain attacks?
A: Frameworks like MITRE ATT&CK’s supply chain tactics (e.g., T1566.002) and NIST’s "Secure the Supply Chain" guidelines integrate third-party risk assessments. Zero Trust frameworks further mitigate risks by enforcing least-privilege access for vendors.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Sac.